
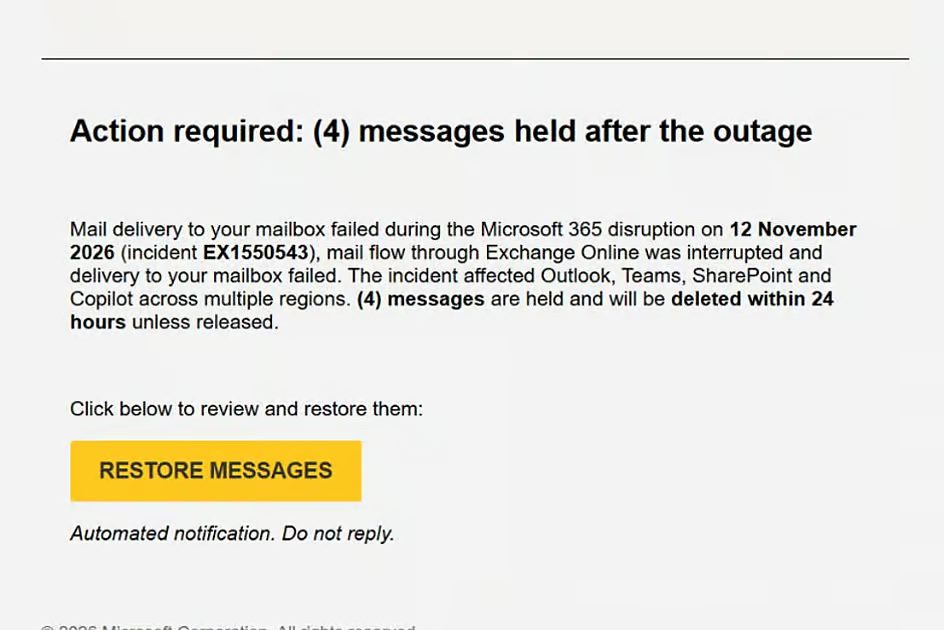
Microsoft Threat Intelligence on Saturday found that an active phishing campaign was exploiting the Microsoft 365 service disruption on November 12.
The messages, it said, impersonate notifications from Microsoft, referencing legitimate Exchange Online incident EX1550543. “Some of the phishing emails Microsoft detected on November 13 falsely claim that messages were held during the outage and will be deleted within 24 hours unless recipients click to restore them.”
It said that observed subjects follow the pattern “Outage – [six-character code],” with sender display names using organisation-specific prefixes followed by “Outage Notification” or “Service Health.”
Stay up to date with the latest news. Follow KT on WhatsApp Channels.
The campaign uses three sender domains, moments-notice[.]com, planetmaison[.]com, and newbooker[.]com, with recipient-specific SendGrid click-tracking links redirecting to reallifeaccounting[.]com, including the observed path /themelist0.html.
It said that similar messages targeted organisations across multiple US sectors, adding that activity is consistent with credential phishing. It also said that credential collection and malware delivery have not been confirmed.
“Security teams can use Microsoft Defender for Office 365 Threat Explorer and Microsoft Defender XDR advanced hunting (EmailEvents, EmailUrlInfo, and UrlClickEvents) to identify suspicious messages, examine embedded URLs, and investigate user clicks.”
Source: Khaleej Times